

In accordance with Cisco Talos, a North Korean‑aligned group has quietly stepped up efforts to focus on crypto job hunters in India with a brand new Python‑primarily based distant entry trojan.
The marketing campaign makes use of pretend job websites and staged interviews to trick candidates into working malicious code. Victims find yourself handing over keys to their wallets and password managers.
Bogus Job Platforms
Job seekers are lured by postings that mimic large names like Coinbase, Robinhood and Uniswap. Recruiters attain out by way of LinkedIn or e-mail. They invite candidates to a “ability‑testing” web site. It feels innocent at first. Behind the scenes, the positioning is gathering system particulars and browser data.
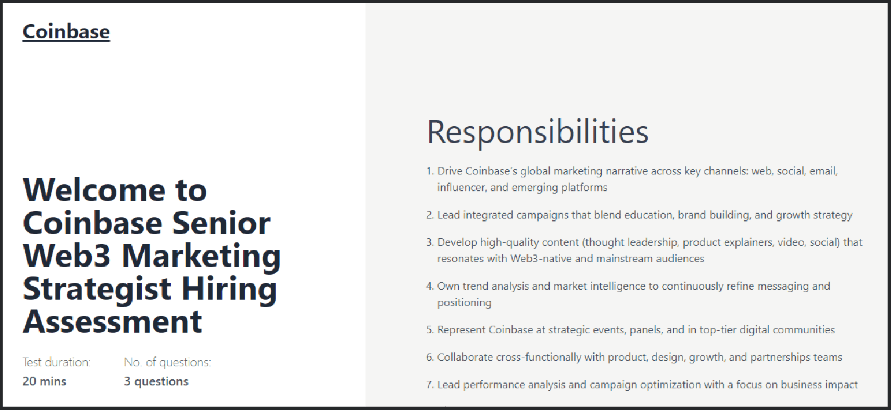
A pattern of a pretend job web site. Supply: Cisco Talos
Misleading Interview Course of
After the check, candidates be a part of a reside video interview. They’re advised to replace their digicam drivers. In a fast transfer, they copy and paste instructions right into a terminal window. One click on and PylangGhost is put in. The entire scheme runs easily—till the malware takes over.
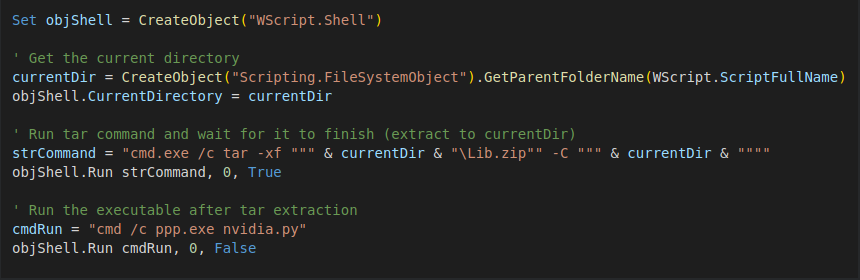
The primary stage merely unzips a Python distribution library and launches the RAT. Supply: Cisco Talos
Superior RAT Instrument
PylangGhost is a spin on the sooner GolangGhost device. As soon as lively, it grabs cookies and passwords from greater than 80 browser extensions. This checklist contains MetaMask, 1Password, NordPass, Phantom, Bitski, Initia, TronLink and MultiverseX.
The trojan then opens a again door for distant management. It will possibly take screenshots, handle recordsdata, steal browser knowledge and maintain a hidden presence on the system.
Historical past Of Comparable Assaults
North Korean hackers used a pretend recruitment check in April earlier than the $1.4 billion Bybit heist. They usually’ve tried related methods with contaminated PDFs and malicious hyperlinks.
This group—referred to as Well-known Chollima or Wagemole—has stolen thousands and thousands by way of crypto pockets breaches since 2019. Their objective is easy: get legitimate credentials after which quietly transfer funds.
Trade Response Measures
Safety groups are on alert. They advocate checking each URL for spelling errors and odd domains. Specialists say to confirm job provides by way of trusted channels.
Endpoint detection instruments ought to flag any script that calls distant servers. And multi‑issue authentication can block stolen passwords from giving full entry.
This alert reveals how far state‑linked actors will go to steal crypto property. The combination of social engineering and customized malware is a potent threat. Anybody looking for work in blockchain ought to double‑examine each hyperlink and by no means run unverified code.
Retaining {hardware} wallets offline and utilizing separate profiles for job looking can reduce down on publicity. Vigilance within the hiring course of and stable technical controls stay the perfect protection in opposition to these evolving threats.
Featured picture from Shutterstock, chart from TradingView

Editorial Course of for bitcoinist is centered on delivering completely researched, correct, and unbiased content material. We uphold strict sourcing requirements, and every web page undergoes diligent overview by our crew of prime know-how consultants and seasoned editors. This course of ensures the integrity, relevance, and worth of our content material for our readers.


