

Current bulletins in quantum computing have introduced renewed consideration to the query of how these advances might impression Bitcoin. In a newly revealed report, we offer an outline of the present state of quantum computing, the risk mannequin for Bitcoin, and the following steps being thought-about. This publish presents a abstract of our key findings and suggestions. See the complete report right here.
Timeline for Bitcoin Preparation to Quantum Computing
We define a dual-track migration technique for Bitcoin in response to the potential emergence of quantum computing.
Lengthy-Time period Path: This complete method assumes that there’s nonetheless a considerable window of time earlier than quantum computing poses a sensible risk. Drawing on the timelines of prior protocol upgrades akin to SegWit and Taproot, we estimate that implementing a full quantum-safe transition might take roughly 7 years.
Brief-Time period Contingency Path: This observe serves as an emergency response within the occasion of a sudden breakthrough in quantum computing. It prioritizes a fast deployment of protecting measures to safe the Bitcoin community and may very well be executed in roughly 2 years.
In each eventualities, funds which are fastidiously managed, i.e., saved in hashed handle sorts like P2PKH or P2WPKH with out handle reuse, are already shielded from quantum assaults. Nonetheless, spending these funds in a post-quantum safe method would require extra infrastructure, which is predicted to be developed in the course of the second part of both timeline
Quantum Computer systems: When Are They Coming, and What Will They Be Succesful Of?
If realized at scale, quantum computing might provide important speed-ups for particular courses of issues by harnessing the ideas of quantum mechanics. Of explicit concern are cryptographically related quantum computer systems (CRQCs), machines able to breaking the mathematical assumptions underlying trendy cryptography. This contains algorithms like Elliptic Curve Cryptography (ECC), which is prime to Bitcoin’s safety.
Whereas quantum computing has been an energetic space of theoretical analysis for many years, important engineering challenges stay in constructing large-scale quantum machines, particularly CRQCs. So far, no quantum laptop has surpassed classical supercomputers in fixing commercially related issues, nor demonstrated the capabilities wanted to threaten trendy cryptography.
Estimated timelines for CRQCs
Technological progress is notoriously arduous to foretell, it hardly ever follows a linear path, and historical past presents many examples of sudden breakthroughs. In anticipation of potential shifts within the cryptographic panorama, a number of organizations have proposed timelines for transitioning cryptographic signatures.
One of the outstanding efforts comes from the U.S. Nationwide Institute of Requirements and Expertise (NIST), which has been main the event of cryptographic requirements. Their revealed suggestions spotlight two key dates:
By 2030, conventional encryption strategies, akin to ECDSA and RSA, ought to be phased out.
By 2035, all cryptographic methods ought to transition totally to post-quantum algorithms.
The UK’s Nationwide Cyber Safety Centre follows a comparable method with a three-phase migration framework that goals to finish the transition to post-quantum cryptography by 2035. Different entities, such because the EU and China, are additionally actively engaged on post-quantum cryptography methods, although they haven’t but revealed formal timelines.
On the trade degree, a number of main corporations, together with Cloudflare, Sign, and Google, have begun adopting post-quantum cryptography. They’re implementing hybrid signature schemes that mix conventional encryption strategies with post-quantum algorithms, requiring an attacker to interrupt each to be able to compromise the system. Apple has additionally introduced plans to transition to post-quantum cryptography. As PQC turns into an rising trade customary, extra corporations are anticipated to observe swimsuit.
What’s at Stake?
The monetary stakes of the risk to Bitcoin are substantial. Fig 2 illustrates evaluation revealing that roughly ~6.51 million bitcoin, value over $700 billion at present valuations, and representing 32.7% of present provide, is quantum susceptible. This contains funds held in addresses which have practiced handle reuse, funds secured by inherently quantum-vulnerable script sorts, and funds which are susceptible by way of public key publicity on forks of Bitcoin, akin to Bitcoin Money.
Bitcoin Menace Mannequin: What Ought to We Be Fearful About?
Quantum computing is predicted to impression two key areas of Bitcoin: mining and transaction signatures. In quantum mining, the problem of mixing the ability of a number of machines offers a disproportionate benefit to massive quantum miners, threatening decentralization. For transaction signatures, the danger is extra direct, a CRQC might derive personal keys from public keys, enabling theft of funds.
Importantly, the timelines for these two threats differ considerably. Constructing a quantum laptop that may outperform trendy ASIC miners presents a far better engineering problem than developing one able to breaking digital signatures. That is due, partially, to the low clock speeds of quantum processors, that are a lot slower than the extremely optimized and specialised {hardware} utilized in Bitcoin mining and the shortage of parallelization.
Signatures
A CRQC might break the idea that it’s infeasible to derive a non-public key from its corresponding public key beneath ECC primarily based schemes, doubtlessly permitting attackers to steal funds. In Bitcoin, possession of a UTXO is confirmed by signing a transaction with the personal key similar to a given public key. If a CRQC can derive that personal key from the general public key, it may well falsely declare possession and spend the funds.
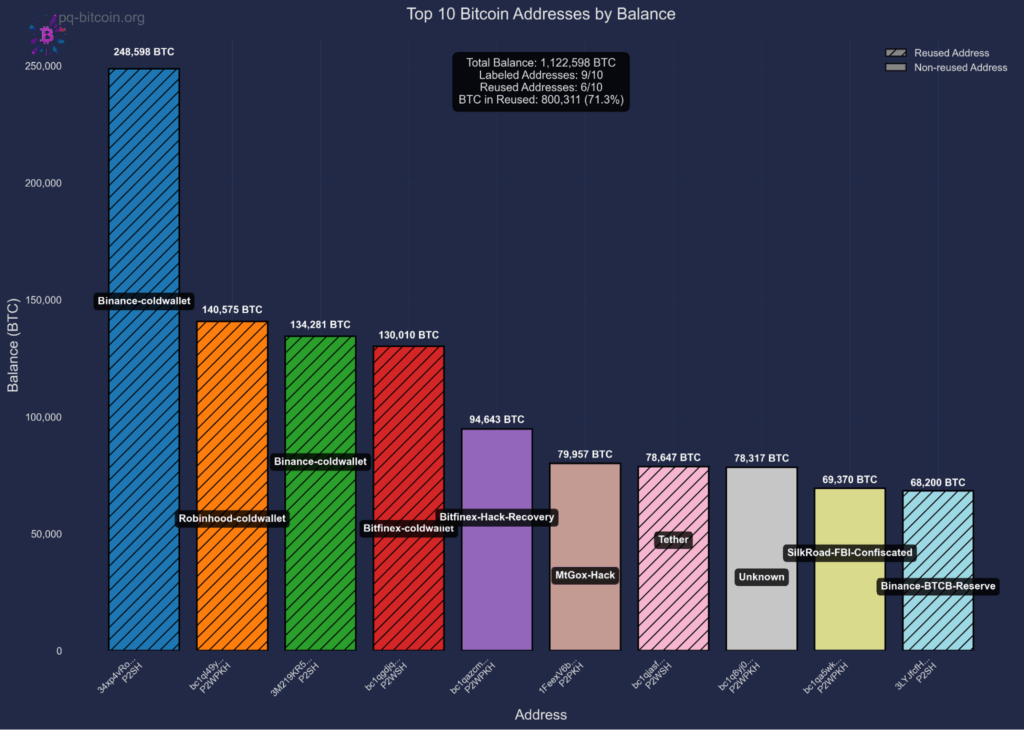
This results in two distinct quantum assault eventualities. When spending from hashed addresses, public keys are revealed briefly, giving attackers a short window, sometimes minutes to hours, to derive personal keys and steal funds, presumably via chain reorganization. In distinction, sure output sorts (P2PK, P2MS, P2TR) expose public keys completely on-chain from the second funds are obtained, giving attackers limitless time to mount quantum assaults. Deal with reuse converts the momentary vulnerability of hashed addresses into everlasting publicity, as public keys stay seen on-chain after the primary spend. As proven in Fig 3, essentially the most susceptible targets are addresses that maintain important funds with uncovered public keys akin to institutional holdings that practiced handle reuse.
Mining
Bitcoin mining relies on the precept that the chance of discovering a sound block scales linearly with the quantity of computational effort expended. Grover’s algorithm, a quantum search method, presents a quadratic speedup for brute-force search. Nonetheless, not like classical mining, Grover’s algorithm just isn’t simply parallelizable. This limitation might give a disproportionate benefit to entities with entry to large-scale, centralized quantum {hardware}, doubtlessly growing mining centralization somewhat than broadening participation.
Along with considerations about centralization, quantum mining might alter miners’ optimum methods, doubtlessly degrading chain high quality, for instance, by growing the speed of stale blocks. A better stale block fee could make sure assaults (akin to egocentric mining or double-spends) less expensive and extra possible.
As famous earlier, constructing a quantum laptop able to outperforming trendy ASIC miners is believed to be a lot farther off than creating CRQCs. As such, quantum mining just isn’t an instantaneous concern and is unlikely to be a sensible risk within the coming a long time. However, exploring Proof-of-Work mechanisms in a future quantum context stays a worthwhile analysis course. Growing a greater understanding of the potential dangers and mitigation methods would assist the ecosystem put together for a world the place quantum mining turns into possible.
Migration to Quantum Safety: What are the primary challenges?
Quantum-Safe Signatures
Quantum-secure cryptographic signatures have been studied for many years, however curiosity and progress have accelerated in recent times. This has led to the event of candidate protocols akin to SPHINCS+, FALCON, and others. Nonetheless, as a comparatively younger area, it has seen a number of proposed schemes initially believed to be safe however have been later damaged (e.g. SIKE), even by classical computer systems. Whereas belief within the present candidates is rising over time, the sphere stays energetic and evolving.
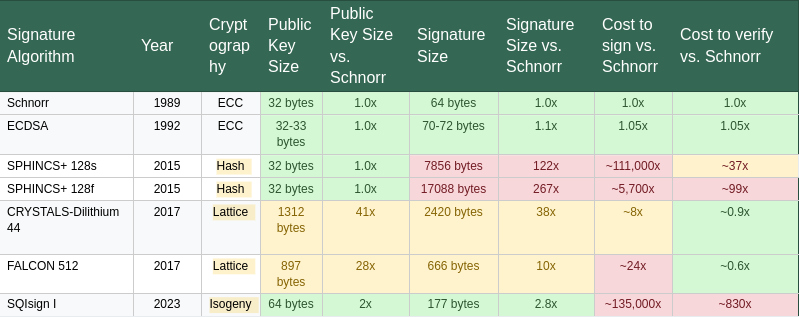
As detailed in Desk 1, a big limitation of post-quantum signature schemes is their considerably bigger key and signature sizes, together with elevated verification instances, relative to classical algorithms akin to ECDSA and Schnorr which are presently utilized in Bitcoin. To handle this, some proposals counsel leveraging SegWit’s witness low cost mechanism to scale back on-chain footprint. Nonetheless, one of the best method for integrating quantum-secure signatures into the protocol stays an open query. Along with efficiency trade-offs, quantum-secure schemes don’t but assist the complete vary of performance supplied by classical signatures, akin to these relied upon within the Lightning Community and different functions. This space continues to be an energetic focus of analysis throughout the cryptography neighborhood, and additional enhancements are anticipated within the coming years.
Migration Pathways
If the Bitcoin neighborhood chooses emigrate susceptible funds to quantum-resistant codecs, numerous UTXOs will have to be moved. A number of approaches are into consideration, every making totally different tradeoffs. Some give attention to enabling safe spending of hashed-address outputs with out exposing the general public key prematurely. Others suggest mechanisms to restrict or regulate the spending of UTXOs which are straight susceptible to quantum theft. These methods typically require adjustments to consensus guidelines, akin to comfortable forks, and should additionally account for the sensible problem of shifting a big quantity of UTXOs, doubtlessly taking 4 to 18 months even with sustained allocation of block house.
Philosophical Dilemma: Can we permit funds to be stolen?
The Bitcoin neighborhood faces a elementary philosophical query: ought to quantum-vulnerable funds be made completely unspendable (“burned”) or stay accessible to quantum computer systems (“stolen”)? This choice touches Bitcoin’s core ideas of property rights, censorship resistance, and immutability. The burn method treats quantum vulnerability as a protocol bug requiring a conservative repair, stopping wealth redistribution to those that win the CRQC race. The steal method maintains that burning funds violates the property rights of their house owners, successfully confiscating belongings from those that might merely be unaware of the risk or unable emigrate in time.
The implications lengthen past philosophy to market dynamics. A coordinated burn would completely take away thousands and thousands of bitcoins from circulation, doubtlessly growing the worth of remaining cash whereas offering market certainty. Permitting quantum theft permits large wealth switch to entities with quantum capabilities, doubtlessly creating extended market uncertainty and volatility as funds are step by step drained. A choice on this matter is a defining second for Bitcoin’s governance mannequin, requiring the neighborhood to stability safety imperatives towards foundational ideas of person sovereignty and non-intervention.
So, what’s subsequent?
The arrival of CRQCs would mark a significant shift throughout the digital panorama, putting a lot of at the moment’s safe communication, authentication, and digital infrastructure in danger. Whereas quantum computing just isn’t but a sensible actuality, preparations are underway to assist guarantee Bitcoin’s resilience towards future developments. Analysis continues throughout each the cryptographic and Bitcoin communities to evaluate potential dangers and discover sensible responses. Our report highlights two areas which will warrant near-term consideration: stopping handle reuse and evaluating the trade-offs within the Burn vs. Steal dialogue round uncovered funds.
The window for proactive motion is open now, although it could not stay open indefinitely. Staying knowledgeable about advances in quantum computing and cryptography is crucial, as is finding out potential mitigation methods and their broader implications for the Bitcoin ecosystem. Making certain Bitcoin’s long-term safety in a post-quantum world requires considerate, deliberate work, beginning now, so we are able to make well-informed selections whereas time continues to be on our aspect.
This can be a visitor publish by Clara Shikhelman and Anthony Milton. Opinions expressed are completely their very own and don’t essentially mirror these of BTC Inc or Bitcoin Journal.


