

Crypto phishing losses plunged in 2025, however consultants warn the menace has solely modified form reasonably than disappeared. Reviews present a pointy fall in cash stolen by wallet-draining scams, at the same time as attackers examined new tips tied to latest protocol adjustments.
Associated Studying
Rip-off Sniffer Information Exhibits Drop
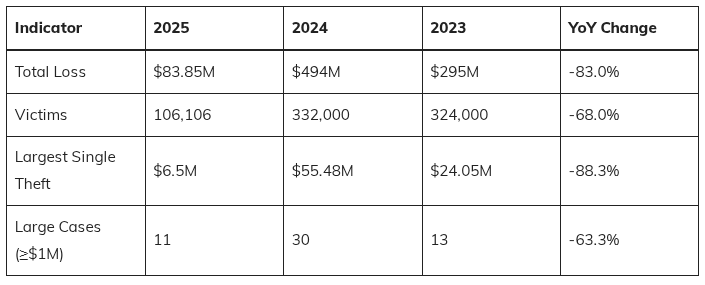
In accordance with Rip-off Sniffer’s 2025 evaluation, pockets drainer phishing losses fell to about $83.85 million — an 83% decline from roughly $494 million in 2024.
The variety of affected wallets dropped to round 106,000, a fall of about 68% year-on-year. These figures come from the safety platform’s annual examine and have been picked up by main crypto retailers.
Attackers Shift, Not Cease
Solely 11 incidents topped $1 million in 2025, down from 30 the prior 12 months, signaling fewer headline grabs however an increase in smaller hits. The biggest single theft recorded final 12 months was roughly $6.5 million, tied to a malicious Allow signature assault.
Common losses per sufferer fell to roughly $790, which suggests attackers moved towards extra frequent, lower-value strikes.
Market Strikes Mattered
Losses adopted market exercise. The third quarter logged the very best injury at about $31 million, when Ethereum’s rally introduced extra customers and approvals onchain.
Month-to-month peaks included August, which posted about $12.17 million, whereas December was the quietest with roughly $2 million. That sample reveals fraudsters goal busy buying and selling home windows.
1/ Ever woken as much as an empty crypto pockets? With scammers draining $107K+ throughout EVM chains JUST THIS WEEK (per @zachxbt), it’s scarier than ever!
Shoutout to @realscamsniffer for his or her 2025 report – losses down 83%, however threats are evolving FAST. Let’s recap & warn on 2026… https://t.co/uSerpsg80d
— JP (@rugpullfinder) January 3, 2026
Allow Signatures And New Vectors
Reviews highlighted Allow and Permit2 signature abuses as a serious driver of massive losses, accounting for a big share of multi-million circumstances.
Rip-off Sniffer additionally flagged EIP-7702 batch signature methods that have been utilized in a number of complicated assaults after community upgrades. Safety groups say these strategies exploit consumer approval flows reasonably than uncooked smart-contract bugs.
Why The Drop Occurred
Analysts attribute a lot of the development to raised pockets warnings, wider use of approval revocation instruments, and extra lively monitoring by onchain screens.
Some defenders additionally level to lowered market froth in components of the 12 months, which lowered the pool of high-value targets. Nonetheless, a number of retailers stress that lowered totals don’t equal security.
Associated Studying
Based mostly on experiences, phishing will seemingly stay cyclical: losses might spike once more throughout massive rallies or when new signing options are launched.
Safety corporations urge customers to examine approvals, keep away from blind signing, and use pockets instruments that flag dangerous requests. Regulators and exchanges are watching the pattern, however duty for a lot of assaults nonetheless falls to particular person customers and pockets software program.
Featured picture from Unsplash, chart from TradingView


