
Scammers are focusing on contributors to the viral AI mission OpenClaw with a complicated phishing marketing campaign aimed toward draining crypto wallets.
By exploiting GitHub’s trusted notification system, attackers lure builders with a pretend $5,000 token airdrop that leads on to a wallet-draining script.
Pretend $5K airdrop targets OpenClaw devs
Scammers used pretend GitHub tags to lure customers to a cloned web site with a hidden pockets join.
Accounts vanished inside hours. No confirmed victims but.
Keep alert
pic.twitter.com/ZYpmckDJ1j
— Bitinning (@bitinning) March 19, 2026
There are not any sensible contract exploits concerned right here. Simply social engineering, leveraging the hype round AI brokers, and unsuspecting customers falling for the lure.
It comes because the broader crypto market suffered a hunch in a single day, with the whole market cap falling 4% to $2.5 trillion, with 24-hour buying and selling quantity sitting at simply over $125Bn.
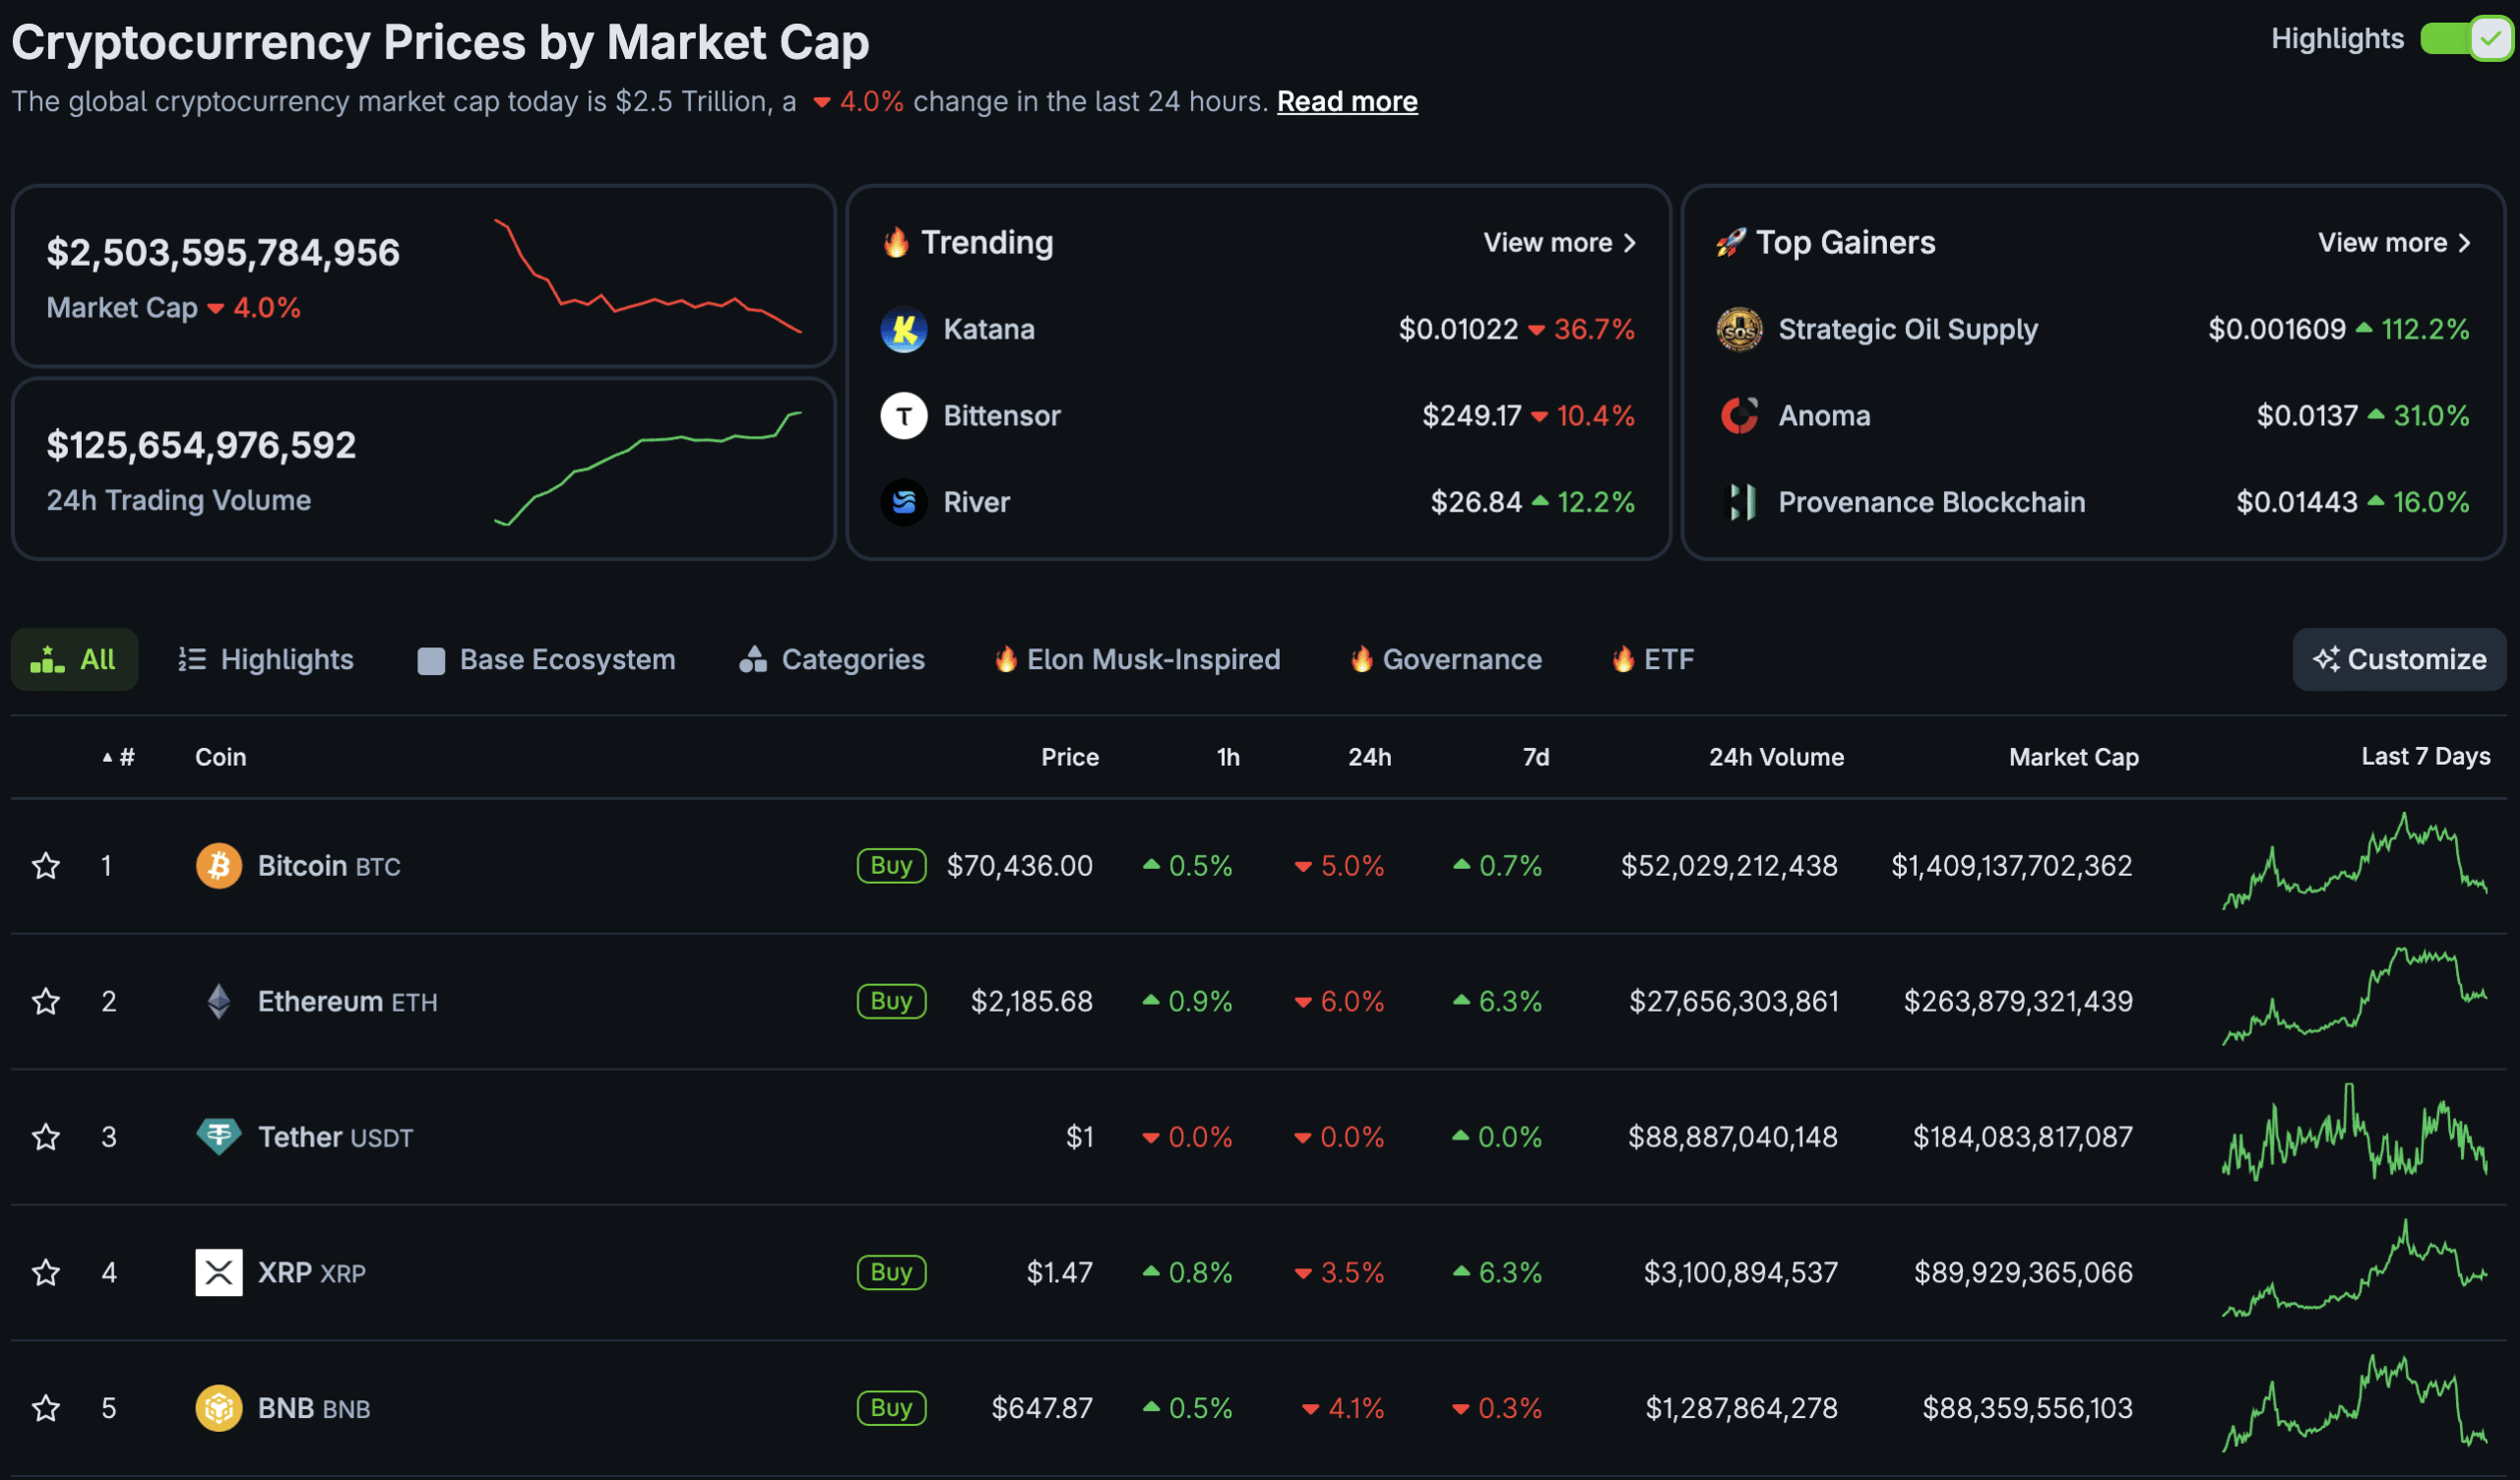
(SOURCE: CoinGecko)
The Lure: Pretend Contributions and Hidden Scripts
In accordance with a report by OX Safety, menace actors create fraudulent GitHub accounts and open difficulty threads in repositories they management. They then tag dozens of genuine OpenClaw builders in these threads.
The message is flattering. It claims, “Respect your contributions on GitHub. We analyzed profiles and selected builders to get OpenClaw allocation.” The scammers promise $5,000 value of $CLAW tokens and direct targets to an internet site that eerily mimics the official openclaw.ai area.
As soon as on the positioning, customers are prompted to “Join your pockets” to say the funds. That is the lure. The positioning executes a connection immediate designed to empty property, powered by a closely obfuscated JavaScript file hidden within the web site’s code named “eleven.js.”
OX Safety researcher Moshe Siman Tov Bustan famous that the marketing campaign intently resembles earlier assaults focusing on the Solana ecosystem on GitHub.
DISCOVER: The Subsequent 1000x Crypto Gem Earlier than It Lists on Exchanges
Why OpenClaw and Why Now?
Peter Steinberger is becoming a member of OpenAI to drive the following era of non-public brokers. He’s a genius with quite a lot of wonderful concepts about the way forward for very sensible brokers interacting with one another to do very helpful issues for individuals. We anticipate it will shortly turn out to be core to our…
— Sam Altman (@sama) February 15, 2026
OpenClaw is presently one of many hottest tech properties. The mission has moved from a developer software to a mainstream AI asset, particularly after OpenAI CEO Sam Altman tapped creator Peter Steinberger to guide the corporate’s push into private AI brokers.
That legitimacy makes it harmful. Scammers know that builders are presently paying shut consideration to the mission. Additionally they know that builders are prone to maintain cryptocurrency and are comfy utilizing Web3 wallets.
This incident highlights a rising pattern the place respectable instruments are used as vectors for theft. It echoes Vitalik Buterin’s considerations about the intersection of AI and pockets safety. As AI instruments turn out to be central to the crypto workflow, the road between useful automation and malicious extraction blurs.
The attackers even seem like utilizing GitHub’s “star” characteristic to construct their goal lists, making certain they go after customers who’ve actively engaged with OpenClaw repositories.
Visualizing the Menace: Quick Protecting Steps
If you’re a developer or energetic GitHub consumer, you might want to lock down your workflow instantly. The sophistication of those clones means visible inspection is usually not sufficient.
Confirm the URL: By no means click on hyperlinks inside GitHub difficulty threads from repositories you don’t acknowledge. At all times kind the official area manually.
Verify the Repo Proprietor: Official airdrops will come from the mission’s most important repository, not a random consumer’s fork. If the repository has few stars or was created lately, it’s a lure.
Use a Burner Pockets: By no means join your most important holding pockets (chilly storage) to any dApp or declare web site. If you’re interacting with a simplified protocol or an airdrop, use a sizzling pockets with minimal funds.
Ignore Surprising Tags: If you’re tagged in a thread by a consumer you don’t know, deal with it as spam immediately. Actual tasks announce allocations on their official X (Twitter) or Discord channels, not through mass-tagging in random points.
DISCOVER: Prime Crypto Presales to Watch Now
Observe 99Bitcoins on X (Twitter) For the Newest Market Updates and Subscribe on YouTube For Each day Professional Market Evaluation.
The publish OpenClaw Builders Hit by GitHub Phishing Assault: Easy methods to Shield Your Pockets appeared first on 99Bitcoins.


