
The decentralized world is thrilling as a result of it offers folks new methods to commerce, create, earn and construct, however with each new expertise additionally comes new risks, and some of the critical threats quietly rising within the background is one thing known as EtherHiding. Many individuals in crypto have by no means heard of it, but specialists in cybersecurity consider it may turn out to be one of many greatest assaults in Web3 historical past.
EtherHiding is a sneaky and highly effective methodology that lets hackers retailer dangerous code inside blockchain good contracts, and since most individuals see good contracts as protected and clear, this type of cyberwarfare threatens the collective thought, long-term adoption and use. Hackers cover harmful malware contained in the very system that’s supposed to guard us, and this twist makes the assault a lot tougher to cease and far simpler for criminals to make use of.
What makes this assault much more horrifying is the way in which it makes use of the issues most alluring about blockchain. It takes benefit of decentralization, permanence, and open entry. These qualities usually set Web3 expertise aside and make it a favorite amongst DeFi customers worldwide, however within the fallacious fingers, they provide hackers a playground that’s nearly unattainable to close down.
How EtherHiding Works
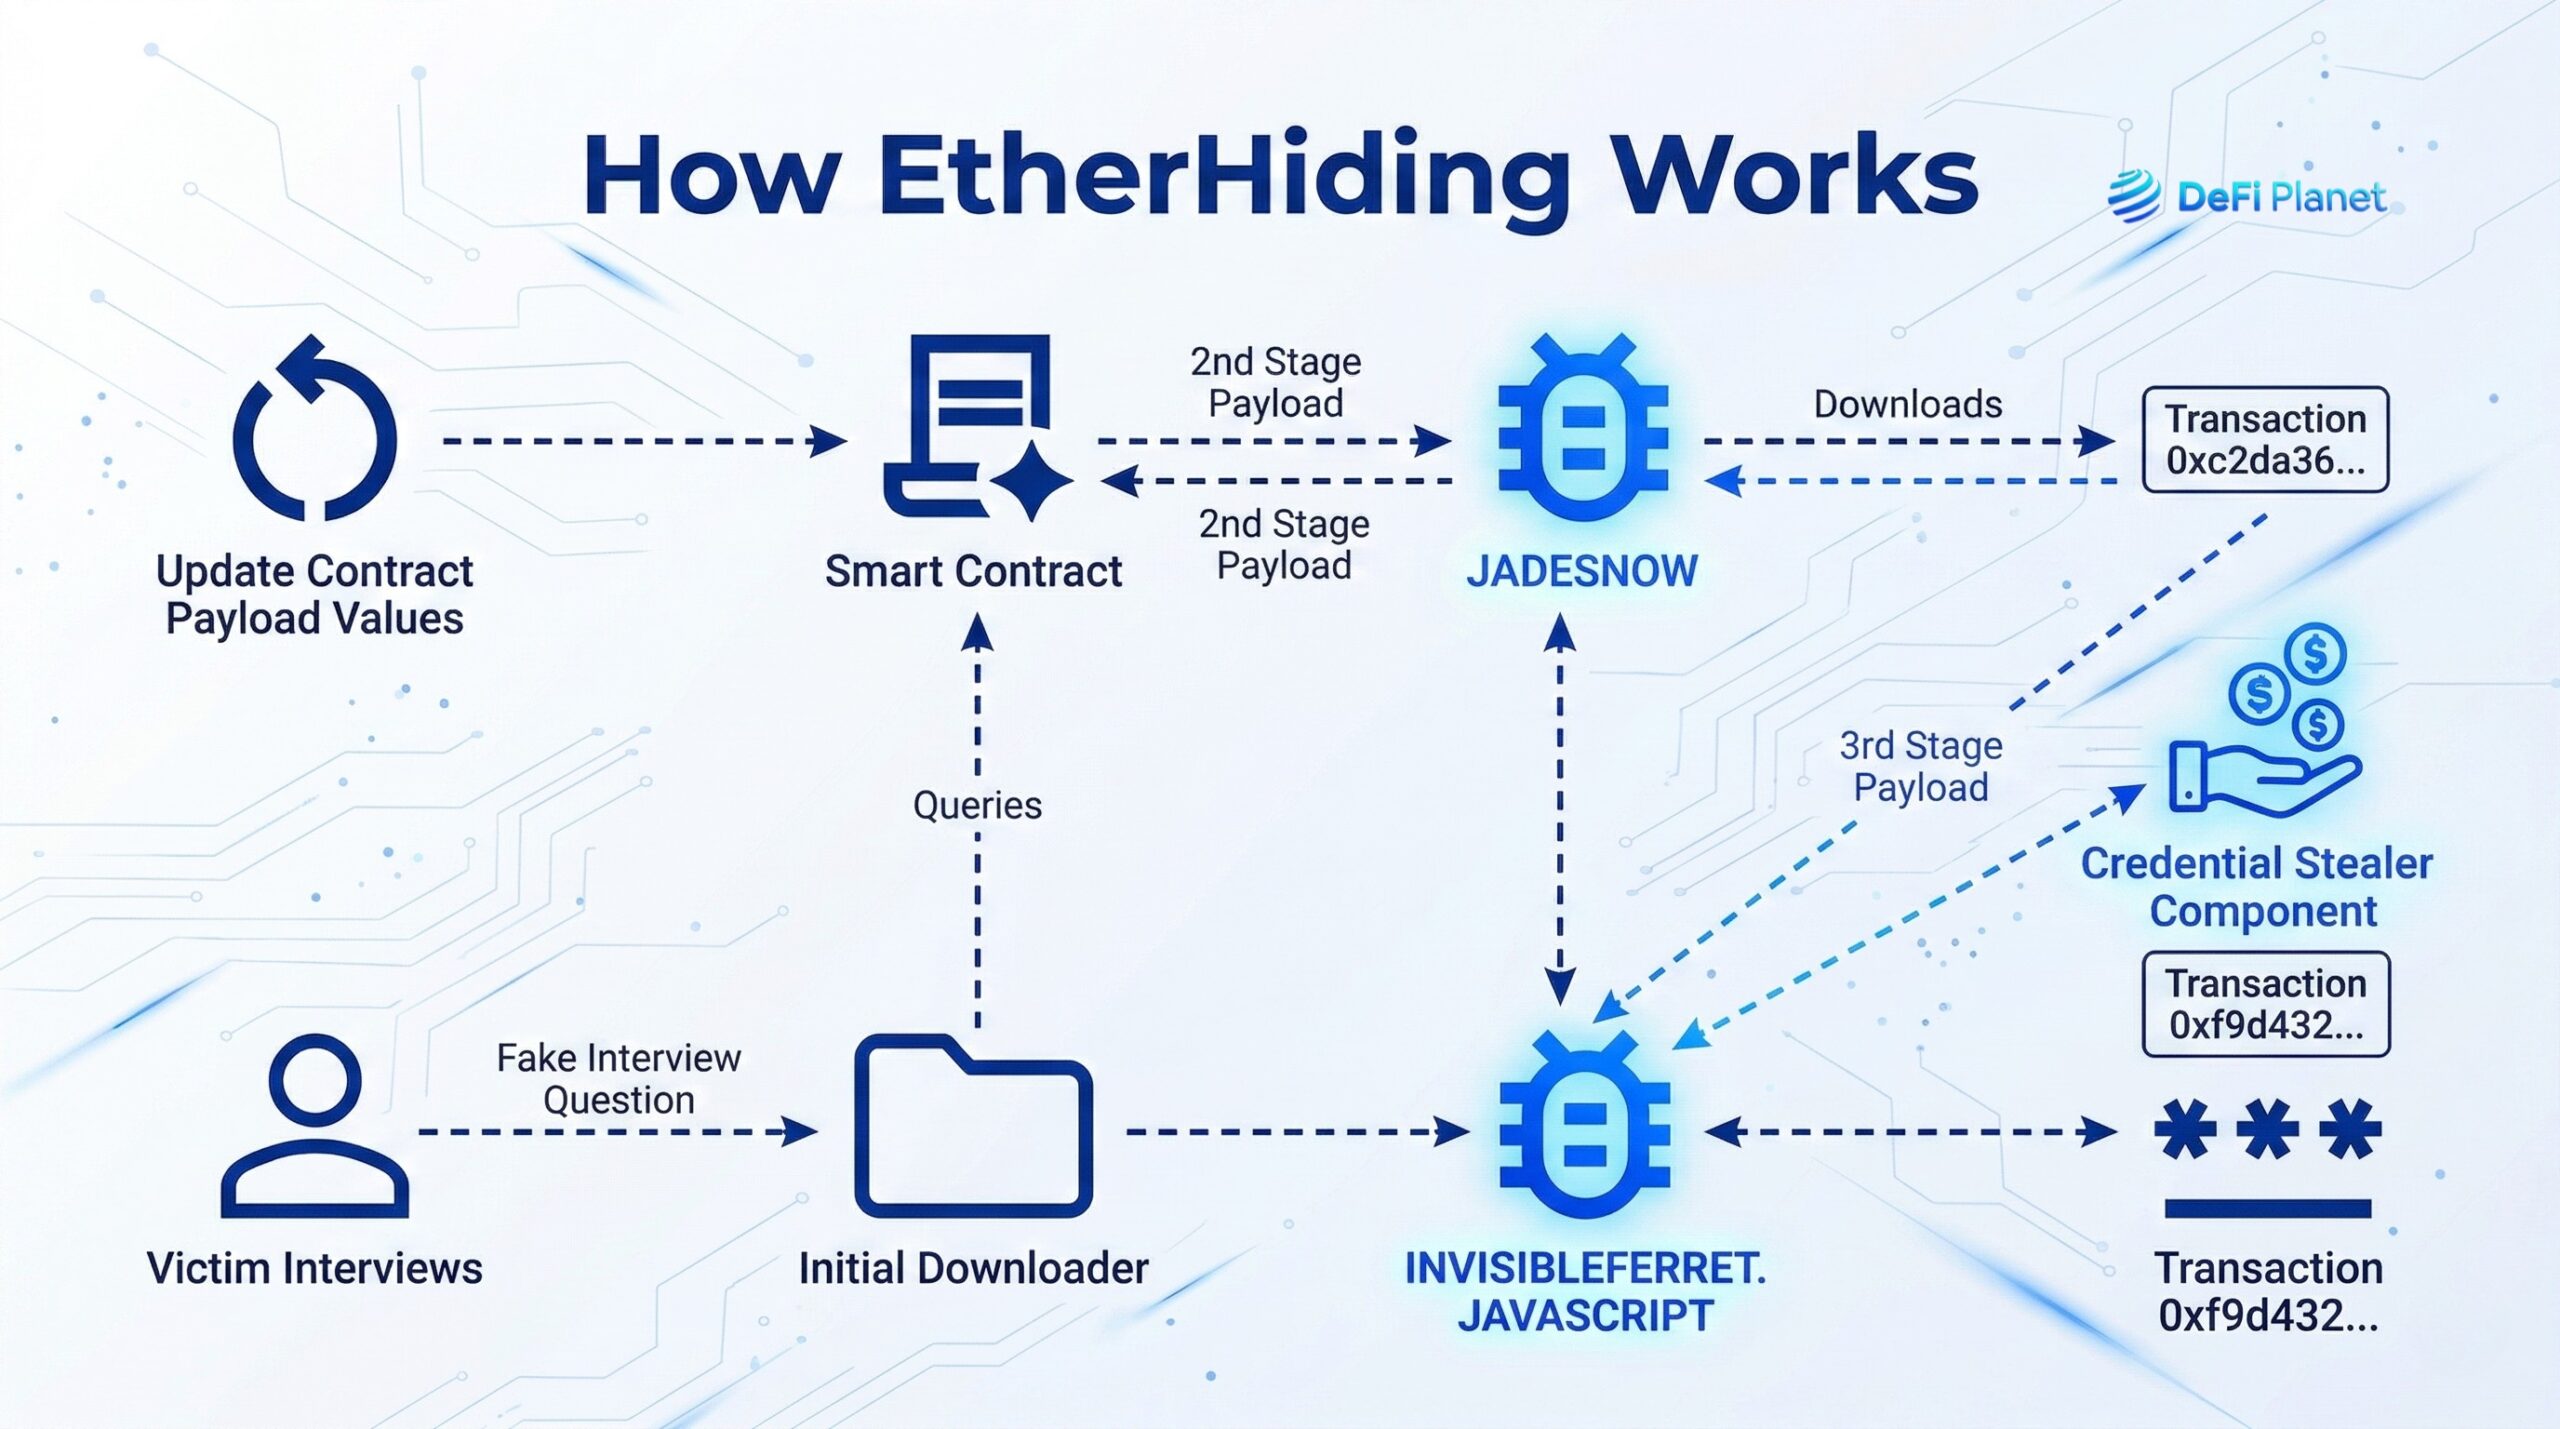
To grasp why EtherHiding is so harmful, think about {that a} hacker desires to cover a dangerous file. Usually, they would wish an internet site or a server, and defenders(cybersecurity personnel) may shut it down as soon as found, however EtherHiding modifications this as a result of as a substitute of internet hosting the dangerous code on a server, the attacker shops it inside a wise contract on a blockchain. As soon as it’s there, deleting it turns into nearly unattainable as a result of blockchains are designed to be everlasting.
The attacker then makes use of small items of knowledge hidden within the contract. When an internet site or pockets interacts with that contract, it secretly pulls these items collectively, they usually kind a dangerous script that may assault the person’s browser and even drain their crypto. This methodology of breaking the code into small chunks makes it very exhausting for safety scanners to note something unusual.
The thought behind EtherHiding works as a result of good contracts enable additional knowledge to be saved inside them. This characteristic was designed to assist builders, however hackers realized it may very well be used as a brand new type of payload supply. As a substitute of conventional malware, the blockchain itself turns into the storage and supply system.
This turns into a nightmare for defenders as a result of good contracts can’t be simply edited or eliminated, and as soon as the dangerous knowledge is positioned there, it stays perpetually. Hackers use this to their benefit, turning the blockchain into a house for code that safety instruments usually can’t detect.
The Position of Sensible Contract Obfuscation

One purpose EtherHiding works so effectively is using good contract obfuscation, and what this implies is that the code is purposefully made obscure. In regular software program, obfuscation is used to guard mental property or delicate logic, however hackers twist that concept and use it to cover their dangerous code.
Sensible contracts can retailer knowledge in some ways: logs, state variables, and even inside faux perform names, however when obfuscation is utilized, the info seems random and innocent. It doesn’t appear to be malware, as it’d seem as meaningless characters, however these characters come collectively to kind an actual assault as soon as loaded by a sufferer.
This methods safety instruments as a result of many scanners deal with contract logic reasonably than hidden knowledge, and that hole offers attackers a secret path to cover harmful scripts contained in the blockchain with out being detected.
The difficulty turns into bigger if you notice that many web sites load knowledge straight from good contracts. NFT platforms, DeFi dashboards, and token trackers all pull info from the blockchain, and if that knowledge comprises obfuscated malware, the web site could unknowingly load it, placing customers in danger.
Why Web3 Safety is Struggling With EtherHiding
The rise of EtherHiding is forcing specialists to rethink how Web3 safety works, as a result of blockchain methods have been constructed on the concept the whole lot is clear and straightforward to examine, and that has been the standing precept behind the expertise. As folks work together with these public contracts, threats must be straightforward to detect, however EtherHiding breaks this perception.
Most Web3 safety instruments test for vulnerabilities like reentrancy or dangerous math logic, however they don’t scan for hidden malware as a result of nobody anticipated attackers to retailer dangerous code inside contract knowledge. This implies EtherHiding slips previous many conventional defence methods to perpetuate its intent.
One other drawback comes from the decentralized nature of blockchains, as a result of in a standard hacking case, defenders can shut down a server or block a site, but when the dangerous code is saved on a blockchain like Ethereum or BNB Chain, nobody can take away it. Not even the platform’s creators.
This offers attackers a degree of management and persistence they by no means had earlier than. It means defenders should adapt and create new methods to scan blockchain knowledge, not simply good contract logic.
EtherHiding and the Way forward for Cyber Threats
Cyber assaults are evolving quickly, and hackers are all the time in search of new methods to remain hidden, persistent, and efficient. The blockchain is engaging to them as a result of it gives precisely what they need; it’s international, everlasting, decentralized and all the time on-line.
This is the reason specialists consider EtherHiding will encourage new types of cyber threats. Hackers could start to construct extra superior methods that unfold dangerous code throughout a number of blockchains, they usually would possibly even create good contracts that replace their hidden malware routinely, or mix EtherHiding with different assaults to create one thing much more highly effective.
We’re coming into a interval the place Web3 and cybersecurity overlap greater than ever, and as DeFi and NFTs turn out to be frequent, hackers see new alternatives to focus on customers by way of the instruments they use daily. Many attackers already use cryptocurrency platforms for cash laundering, phishing and pockets draining, however EtherHiding offers them one thing much more harmful. It offers them a spot to cover their code that defenders can’t simply contact.
How Customers Turn into Targets
Many customers suppose they’re protected so long as they keep away from clicking suspicious hyperlinks or downloading unusual information, however EtherHiding breaks this concept utterly. With this assault methodology, you’ll be able to turn out to be a goal simply by visiting an internet site that hundreds blockchain knowledge, and if that knowledge comes from a good contract obfuscation method that hides dangerous code, your browser could run the script with out you ever realizing what occurred.
Folks belief Web3 web sites as a result of they consider the whole lot is clear on the blockchain and that dangerous scripts could be straightforward to identify, however EtherHiding is completely different: attackers place the code inside a wise contract that appears regular at first look. Safety groups name this silent payload supply, and it is without doubt one of the hardest issues in Web3 safety right now.
Identified Assaults That Used EtherHiding
One notable cyber assault marketing campaign that used EtherHiding is the “ClearFake” marketing campaign, the place cybercriminals compromised WordPress-based web sites by injecting hidden JavaScript code into article pages.
In one other case, EtherHiding was used with Pretend-Updates, a tactic the place customers have been tricked into downloading malware disguised as software program updates. Victims have been offered with pop-ups prompting them to obtain what seemed to be reliable updates, however these truly delivered malicious code by way of the blockchain, resulting in web site defacement and malware infections.
What Defenders Want To Do Subsequent
Defending in opposition to EtherHiding requires a brand new mindset; builders and safety groups have to deal with good contract knowledge as a possible assault floor, they usually should scan not solely the logic but additionally the saved values that may cover obfuscated code.
Entrance-end builders have to sanitize and filter the info they load from contracts; they can’t assume blockchain knowledge is protected simply because it’s on-chain, and pockets suppliers might also want so as to add warnings when a contract comprises suspicious knowledge patterns. Safety firms will want new instruments that scan for hidden malware throughout completely different chains.
Most significantly, the Web3 neighborhood should educate itself as new threats require new habits and new defensive pondering. If folks perceive EtherHiding, they’ll learn to shield themselves and assist the ecosystem develop safely.
Last Ideas
The rise of EtherHiding reveals the world that the blockchain is not only a platform for finance and creativity; additionally it is a battleground for superior hackers who wish to use its energy for dangerous functions. By hiding malware inside good contracts and utilizing good contract obfuscation to disguise it, attackers have discovered a approach to outsmart previous defences.
This menace issues as a result of it challenges the whole lot Web3 believes about transparency and security, it forces a brand new understanding of Web3 safety and opens the door for future cyber threats that use the blockchain itself as a payload supply system.
The hazard is actual, however so is the chance to construct stronger defences; if builders, customers and safety researchers be a part of collectively and put together for these assaults, Web3 can turn out to be safer and extra resilient.
Disclaimer: This text is meant solely for informational functions and shouldn’t be thought of buying and selling or funding recommendation. Nothing herein must be construed as monetary, authorized, or tax recommendation. Buying and selling or investing in cryptocurrencies carries a substantial threat of economic loss. All the time conduct due diligence.
Loved this piece? Bookmark DeFi Planet, discover associated subjects, and observe us on Twitter, LinkedIn, Fb, Instagram, Threads, and CoinMarketCap Neighborhood for seamless entry to high-quality business insights.
Take management of your crypto portfolio with MARKETS PRO, DeFi Planet’s suite of analytics instruments.”


